The Cabinet Office's own rulebook says every government grant shall get a fraud risk assessment. Its own auditor found most schemes have never measured whether they lost any money at all, and there is no penalty for departments that fail the standard outright.
Estimated reading time: 6 minutes
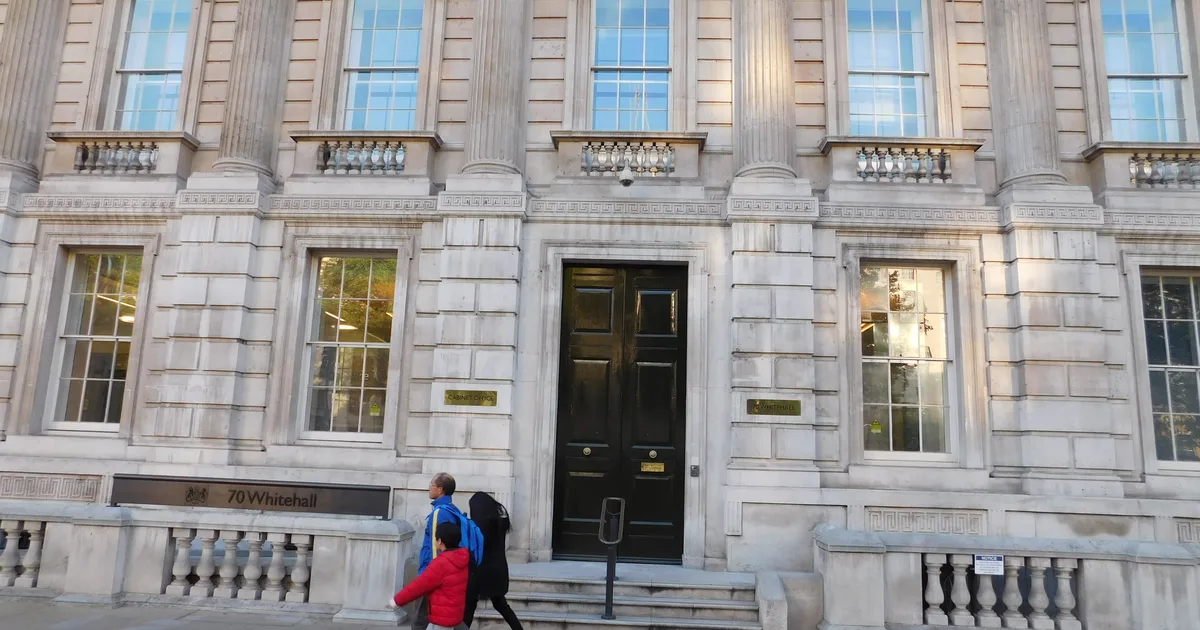

In short. Government Functional Standard GovS 015: Grants states, as a mandatory requirement, that "all government grants shall be subject to timely and proportionate due diligence, assurance and fraud risk assessment." The National Audit Office's July 2024 audit of general grant schemes found that not all schemes have carried out a fraud risk assessment at all, most have never measured their actual losses, assurance and counter-fraud are two of the four weakest things departments admit to in their own compliance scoring, and there is no sanction for a department that misses the standard's pass mark altogether. Three documented mistakes: four stars.
On 15 September 2026 the Cabinet Office made its fourth change of the year to the page for Government Functional Standard GovS 015: Grants, swapping in a link to a newer version of the tool departments use to mark their own compliance. The standard underneath has not changed its central promise since it was first published on 2 December 2016: that setting expectations for how government hands out grants will "promote efficient and effective grant making" and deliver "value for money through high quality delivery" [1]. The government's own auditor has already tested that promise against general grants worth £46.8 billion in 2022-23 alone, 4% of everything central government spent that year [3], and found that the one part of the standard written as compulsory, not aspirational, is the part departments are worst at keeping.
The claims, tested
| The document's own words | What the record actually shows | Verdict |
|---|---|---|
| GovS 015, Minimum Requirement Seven ("Risk, Controls and Assurance"): "All government grants shall be subject to timely and proportionate due diligence, assurance and fraud risk assessment" [2] | The National Audit Office, paragraph 16 (page 12): "not all schemes have carried out a fraud risk assessment, most schemes have not measured actual losses, and, where measurements have been carried out, they have been of variable quality" [4] | The one requirement the standard states in "shall" language, not guidance, is the one the government's own audit found routinely unmet |
| GovS 015's purpose statement: to "promote efficient and effective grant making" and ensure "value for money through high quality delivery" [1] | NAO, paragraph 2.7 (page 32): departments must score at least 40% on self-assessment to be rated "good"; "there are no sanctions for organisations that do not meet this threshold" [4] | A standard that promises value for money has no working mechanism to compel a failing department to deliver it |
| Grants Continuous Improvement Assessment Framework V2, "comply or explain" principle: "an organisation is permitted to mark an individual criterion as met, where a rationale is provided that clearly explains why the organisation is not able to meet the criterion either partly or in full" [5] | The rationale is checked by the Grants Management Function, the same central team that owns and promotes the standard, "to ensure that the rationale provided is reasonable" [5]; NAO separately notes it is the Government Internal Audit Agency, not the Grants Management Function, that validates the numeric self-assessment scores (paragraph 2.6, page 32) [4] | A department can be marked as meeting a requirement it has not met, if the standard's own custodian accepts its explanation |
The mistakes, counted
A mandatory fraud check that most schemes have never carried out (1). GovS 015's Minimum Requirement Seven does not hedge: "all government grants shall be subject to timely and proportionate due diligence, assurance and fraud risk assessment" [2]. The National Audit Office checked this directly against the requirement's own 2016 origin: "one of the minimum standards for grants, set by the Cabinet Office in 2016, is that all grant schemes are subject to a timely and proportionate fraud risk assessment. However, not all schemes have carried out a fraud risk assessment, most schemes have not measured actual losses, and, where measurements have been carried out, they have been of variable quality" [4]. Where losses have been measured, they ranged from under 0.1% to 10.2% of a scheme's value [4]. The Grants Management Function's own estimate is that 20% of the up to £1.9 billion a year it believes better grant management could save, close to £380 million, sits specifically in unrealised improvements to risk, control and assurance [4]. Eight years after the requirement was set, the government's own figures say it does not know how much of that money has actually gone missing.
A pass mark with nothing behind it, missed most by the departments with the most to spend (2). Departments are expected to score at least 40% in self-assessment to be rated "good", the standard's stated minimum expectation [4]. In the most recent assessment, 14 of 15 departments met it; the Department for Levelling Up, Housing & Communities did not, and "there are no sanctions for organisations that do not meet this threshold" [4]. The gap between the best and worst-performing departments has meanwhile widened, from 33 percentage points in 2018-19 to 52 points in 2021-22 [4]. The auditor's own words for who sits at the bottom of that gap: "some departments which manage the largest grant portfolios are among those with the lower grant capability. This is the opposite of what we would expect" [4], naming the Department for Education and the then Department for Levelling Up, Housing & Communities, two of the four biggest general-grant spenders, as consistent low scorers. Assurance (47%) and counter-fraud (52%) were two of the four lowest-scoring areas of grant management self-assessed anywhere in government, alongside the skills and experience of the people doing the assessing (42%) [4].
Compliance a department can write for itself (3). Since 21 May 2026, GovS 015's own page has linked departments to the Grants Continuous Improvement Assessment Framework V2, revised again on 27 July 2026 and re-linked on 15 September 2026, the update that put this standard back in front of trackedchanges this week [5]. Its "comply or explain" principle states plainly that "an organisation is permitted to mark an individual criterion as met, where a rationale is provided that clearly explains why the organisation is not able to meet the criterion either partly or in full" [5]. That rationale is checked by the Grants Management Function itself, the body that owns, promotes and is scored on the success of the standard, not by the Government Internal Audit Agency that the NAO credits with validating the numeric self-assessment scores more generally [4] [5]. A department can be marked "met" on a requirement it has not met, checked by the same office whose job is to say the standard is working.
Credit where due
Grant capability has genuinely improved: the median self-assessment score across departments rose from 46% in 2018-19 to 66% in 2021-22, climbing every year including through the COVID-19 grant surge [4]. The £166 million to £332 million in savings the Grants Management Function claims from 2020-21 to 2022-23 was independently audited by the Government Internal Audit Agency using a sampling methodology, real external verification, not self-marking [4]. Its Complex Grants Advice Panel reviewed the design of 62 of government's highest-value schemes, worth £38.6 billion, in 2023-24 alone, with 78% of its 417 recommendations accepted or partly accepted [4], real engagement with the money most at risk. And the "comply or explain" principle does require a written rationale reviewed against the evidence, not an unchecked box, even if the reviewer is not independent of the standard it is checking.
Verdict
Four stars, from three documented mistakes. GovS 015 states as a mandatory, "shall" requirement that every government grant gets a fraud risk assessment; the government's own auditor found most schemes have never measured whether they lost anything at all. The standard sets a pass mark for basic compliance; missing it carries no sanction, and the departments most likely to miss it are, on the auditor's own account, the ones spending the most. And the self-assessment framework that is supposed to police all of this lets a department mark itself compliant on a requirement it has not met, so long as the standard's own custodian accepts the excuse. Grant capability has improved and some of the savings are real and independently checked. Whether the money that specifically depends on fraud controls, the one thing the standard says "shall" happen, is safe remains, by the government's own figures, unmeasured.
Sources
- Government Functional Standard GovS 015: Grants, GOV.UK / Cabinet Office, published 2 December 2016, updated 15 September 2026
- GovS 015: Minimum Requirement Seven, Risk, Controls and Assurance, GOV.UK / Cabinet Office
- Government's general grant schemes, National Audit Office, HC 126, published 23 July 2024
- Government's general grant schemes (full report, PDF), National Audit Office, HC 126, published 23 July 2024
- Grants Continuous Improvement Assessment Framework V2, GOV.UK / Cabinet Office, added 21 May 2026, updated 27 July 2026